On-premise
Ironbridge Corporate data center
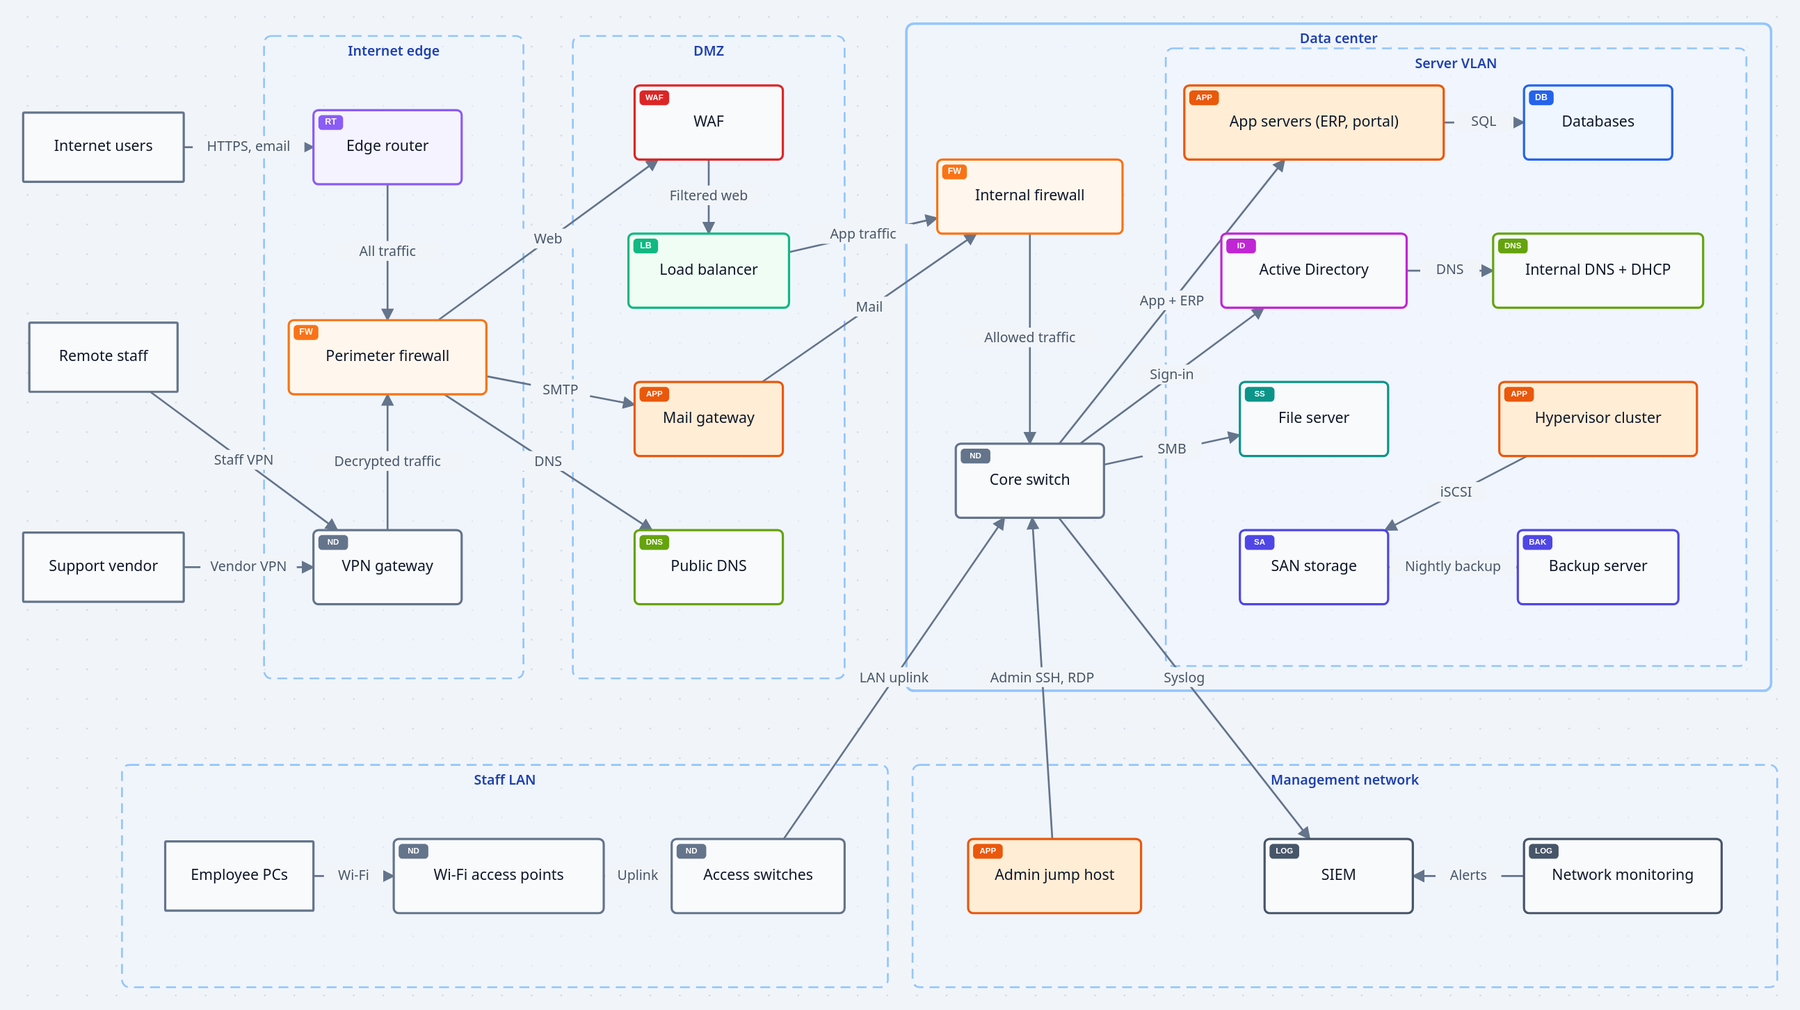
A company that runs its IT in its own server room. An edge router and perimeter firewall face the internet, with a VPN gateway for staff and a support vendor. A DMZ holds the WAF, load balancer, mail gateway and public DNS. Behind the internal firewall are the core switch, Active Directory, internal DNS and DHCP, app servers, databases, file server, hypervisors, SAN and backups, plus a staff LAN and a management network.
- Routers
- Firewalls
- VPN gateway
- Load balancer + WAF
- Core + access switches
- Wi-Fi
- Active Directory
- Hypervisors
- SAN
- Backups
- SIEM
Key risks in the model
| Threat | Score | First fix |
|---|---|---|
| Ransomware reaches servers and backups | 20 Critical | Keep an immutable or offline backup copy off site |
| Flat network: any PC can reach every server | 16 Critical | Route between VLANs through the internal firewall |
| An unpatched VPN gateway gives direct access | 15 High | Patch internet-facing devices within days of a critical advisory |
| Shared admin password on firewalls and routers | 15 High | Named admin accounts through central sign-in with MFA |
1 data flow diagram · 2 attack trees · 12 scored risks (3 critical)