Free threat modeling templates

A data flow diagram, an attack tree and a STRIDE risk register, each filled in with a worked example so you can see how it's meant to be used. Download them, relabel them for your system, and use them in the tools you already have open.

  • No signup, no email
  • Open formats: .drawio and .csv
  • Free for commercial use

What is a threat modeling template?

A threat modeling template is a ready-made starting file for one of the artefacts a threat model needs. These free templates are a data flow diagram and an attack tree for draw.io, and a STRIDE risk register as a CSV file that opens in Excel or Google Sheets, each with example content you replace with your own system.

Free templates

Pick a template and start today

Each file is a complete worked example, not a blank shell. Download it directly, or open its page for a walkthrough of every element.

Free.drawio · 5 KB

Data Flow Diagram Template

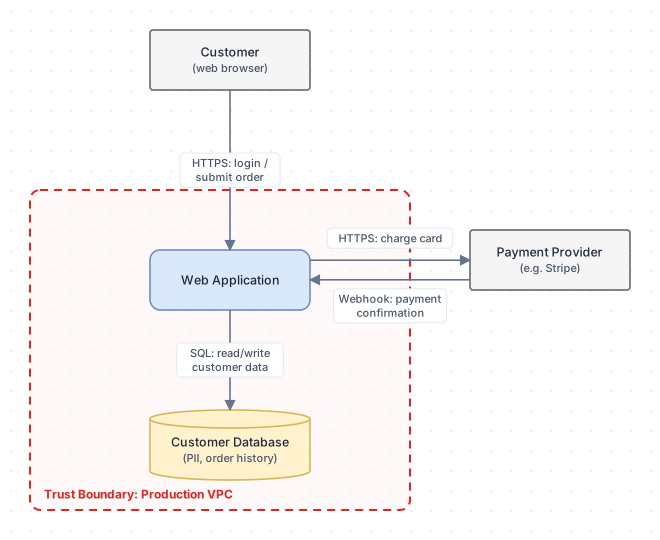
A web app with a customer, a payment provider, a database and a trust boundary, connected by labelled data flows.

  • All four DFD element types, with a legend
  • A trust boundary around production
  • Opens in draw.io, web or desktop
Free.drawio · 6 KB

Attack Tree Template

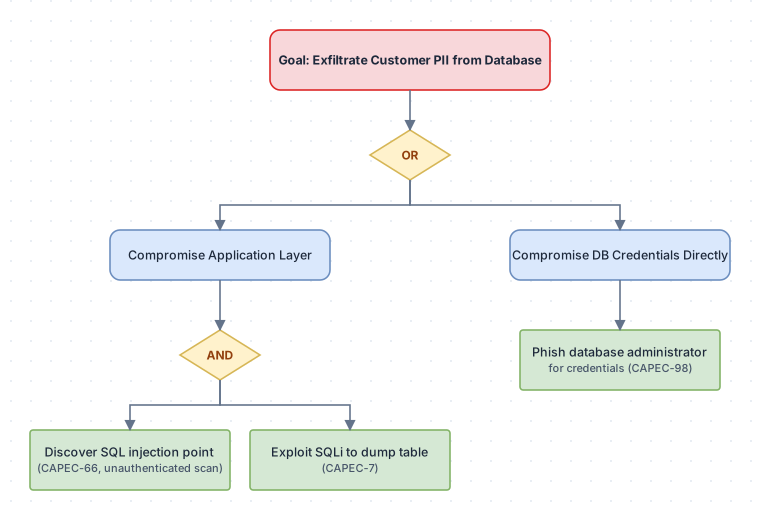
"Exfiltrate customer PII from the database", decomposed through OR and AND gates into concrete attack steps.

  • Goal, sub-goals, OR and AND gates
  • Leaf steps tagged with CAPEC IDs
  • Opens in draw.io, web or desktop
Free.csv · 2 KB

Risk Register Template

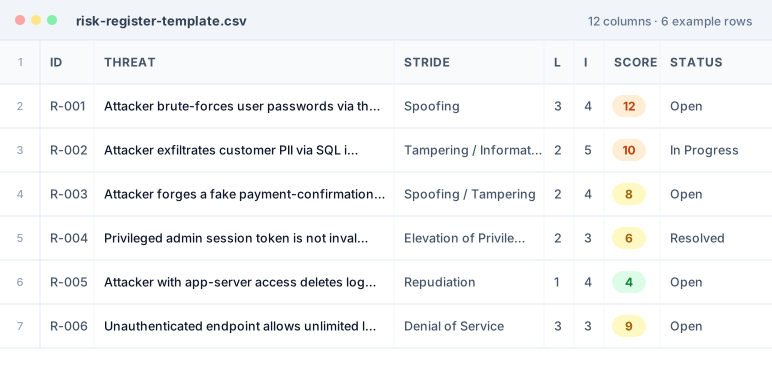
Twelve columns and six example rows that cover every STRIDE category, scored on likelihood × impact.

  • STRIDE category and 1–25 risk score
  • Mitigation, owner, status, review dates
  • Opens in Excel, Sheets, Numbers
How they fit

Use them in order

The three templates are one workflow. Each step feeds the next, which is what turns a diagram into decisions.

1Data flow diagram

Agree what the system is

Draw the components, the data moving between them and the trust boundaries it crosses. Most threats sit where data crosses a boundary.

How to build a DFD →

2Attack tree

Work out how it breaks

For each threat that matters, decompose the attacker's goal into the steps they need. One control that blocks several branches is your best fix.

What is an attack tree? →

3Risk register

Decide and assign

Score each threat, choose a mitigation, name an owner and set a review date, so accepted risk is a decision rather than a silence.

From threat model to register →
Free in ThreatTree

Or start from a finished threat model

Five complete models, free on every plan: a data flow diagram, two attack trees and a scored risk register with owners and treatments. Pick the one closest to how your system is built, then relabel it.

On-premise

Ironbridge Corporate data center

A company's own network: edge router, firewalls, a DMZ with a load balancer, switches, Wi-Fi, Active Directory, hypervisors, SAN and backups.

  • Firewalls
  • Routers
  • Load balancers
  • Active Directory

Covers: Flat networks, unpatched VPN gateways, ransomware reaching backups.

1 DFD · 2 attack trees · 12 scored risks

Shared hosting + AI

Quillpad AI writing assistant

Laravel and MySQL on a Hostinger or GoDaddy-style hosting plan, calling the OpenAI API, with Stripe and SMTP email.

  • Shared hosting
  • MySQL
  • OpenAI API
  • Stripe

Covers: Downloadable .env files, panel takeover, web shells, a runaway AI bill.

1 DFD · 2 attack trees · 12 scored risks

AWS + AI

Lexibase AI document assistant

Multi-tenant RAG on Amazon Bedrock: CloudFront, Cognito, API Gateway, ECS Fargate, an S3 to Lambda ingest pipeline and OpenSearch.

  • AWS
  • Bedrock
  • Cognito
  • S3
  • Lambda

Covers: Cross-tenant retrieval, SSRF to task credentials, loose GitHub OIDC trust.

1 DFD · 2 attack trees · 10 scored risks

Azure + Google Cloud

Teamscope People analytics

Entra ID sign-in and the app on Azure; BigQuery and Gemini on Google Cloud, joined by workload identity federation.

  • Azure
  • Google Cloud
  • Entra ID
  • BigQuery
  • Vertex AI

Covers: nOAuth, any-tenant sign-in, static keys, logs split across clouds.

1 DFD · 2 attack trees · 10 scored risks

Simple

Invoicely SaaS invoicing app

The basics, worked through in our walkthrough: a web API, an admin console, Stripe payments and file storage.

  • Web API
  • Postgres
  • Stripe
  • File storage

Covers: Credential stuffing, IDOR, forged payment webhooks.

1 DFD · 2 attack trees · 10 scored risks

Each opens as a draft. It isn't added to your forests, or counted in the Free plan's 3, until you choose to save it. See every example in detail →

Pro & Enterprise

Industry templates, ready to open in ThreatTree

A complete worked model for a representative system in your industry: the diagram, attack trees and register already linked together. Open one as a forest and adapt it, instead of starting from a blank canvas. Included on Pro and Enterprise.

The Fintech template's attack tree in ThreatTree: the goal Move Funds Without Authorization splits through an OR gate into Account Takeover (credential stuffing and SIM swap MFA bypass) and Forged Webhook (unsigned webhook and forged payment event)
Attack tree

Fintech Payment Flow

A tokenized card-payment flow scoped around a PCI DSS cardholder data environment, with account takeover and forged webhooks decomposed as attack paths.

DFD1 attack tree4 scored risks
Or download:
Fintech threat modeling guide →
The Healthcare template's data flow diagram in ThreatTree: patients and clinicians reach a Patient Portal and an Access Gateway inside a Covered Entity Network (HIPAA scope) boundary, which feed the EHR Core, EHR Database and an HL7/FHIR engine connected to Lab and Imaging
Data flow diagram

Healthcare EHR

An electronic health record system inside a HIPAA covered-entity boundary, with insider snooping and interface-engine compromise as attack paths.

DFD1 attack tree3 scored risks
Or download:
Healthcare threat modeling guide →
The AI Agent Pipeline template's data flow diagram in ThreatTree: an Agent Orchestrator and Hosted LLM inside a Context Window boundary, with input and output guardrails, a RAG retriever and vector store, agent memory, an MCP tool server with a human approver, and a fine-tuning pipeline
Data flow diagram

AI Agent Pipeline

A RAG agent with long-term memory, MCP tools behind human approval and guardrails, with agent hijacking and data exfiltration tagged to the OWASP LLM Top 10 and MITRE ATLAS.

DFD2 attack trees11 scored risks
Or download:
AI & ML threat modeling guide →
The Automotive template's data flow diagram in ThreatTree: a driver app, telematics backend, OTA update server and signing keys in the OEM cloud, connected over cellular to a vehicle network where a central gateway sits between the infotainment and telematics units and the brake and powertrain ECUs
Data flow diagram

Connected Vehicle TARA

A connected car for a TARA: telematics, infotainment and a central gateway in front of the safety buses, with remote commands and over-the-air updates. Unauthorised vehicle commands and malicious firmware are decomposed and mapped to ISO/SAE 21434.

DFD2 attack trees9 scored risks
Or download:
Automotive threat modeling guide →
The Medical Device template's attack tree in ThreatTree: the goal Deliver an unsafe insulin dose splits through an OR gate into impersonating the app (pairing without authentication and replayable bolus commands), spoofed CGM readings, malware on the patient's phone and malicious firmware, each tagged with STRIDE, CAPEC or OWASP categories
Attack tree

Connected Insulin Pump

An insulin pump and CGM sensor controlled from a phone app over Bluetooth LE, with a clinic portal and an EHR feed. Unsafe dosing and exposure of health data are decomposed, with the cloud-side risks mapped to HIPAA.

DFD2 attack trees9 scored risks
Or download:
Medical device threat modeling guide →
The Critical Infrastructure template's data flow diagram in ThreatTree: enterprise IT, an OT DMZ with a jump host and plant historian, a SCADA control network with an engineering workstation and operator HMI, and a field network with a safety system, dosing PLC and pump station RTU
Data flow diagram

Water Treatment Plant OT

A water treatment plant laid out as Purdue levels, from IT through the OT DMZ to the PLCs and safety system. Unsafe chemical dosing and plant shutdown are decomposed with ATT&CK for ICS techniques and mapped to IEC 62443 and NERC CIP.

DFD2 attack trees10 scored risks
Or download:
Critical infrastructure threat modeling guide →
The Electricity Grid template's data flow diagram in ThreatTree: corporate IT, a control centre DMZ with a jump host, SCADA historian and ICCP gateway to the TSO, a control centre with the SCADA / ADMS server, engineering workstation and operator HMI, and a primary substation with a firewall, gateway RTU, station HMI, protection relays, bay controller and GPS clock
Data flow diagram

Electricity Grid & Substation OT

A distribution control centre and an IEC 61850 primary substation reached over IEC 104. Outages, delayed restoration and defeated protection are decomposed with ATT&CK for ICS techniques from the Ukraine grid attacks, and mapped to IEC 62443 and NIS2.

DFD3 attack trees16 scored risks
Or download:
Critical infrastructure threat modeling guide →
The Pharma Manufacturing template's data flow diagram in ThreatTree: ERP and corporate AD in IT, an OT DMZ with a jump host, recipe and order broker and patch server, the MES, historian and engineering workstation at level 3, and a production cell with an ISA-88 batch server, line HMI, bioreactor, filling and safety PLCs and a machine builder's 4G router
Data flow diagram

Pharma Manufacturing Plant OT

A pharmaceutical plant by Purdue level, from ERP and the MES down to the bioreactor, filling line and safety PLCs. Batch tampering with GMP data integrity, ransomware and supplier access are decomposed with ATT&CK for ICS and mapped to IEC 62443 and NIS2.

DFD3 attack trees16 scored risks
Or download:
Critical infrastructure threat modeling guide →
The SaaS template's attack tree in ThreatTree: the goal Read another tenant's data splits through an OR gate into a missing tenant filter, an unvalidated SAML assertion, support console over-reach, a shared cache key collision and a leaked export link, each tagged with STRIDE, OWASP or CAPEC categories
Attack tree

B2B SaaS Platform

A multi-tenant B2B platform with SAML SSO and SCIM, a support console, customer webhooks and a CI/CD deploy role. Cross-tenant access and production compromise are decomposed and mapped to SOC 2 criteria.

DFD2 attack trees10 scored risks
Or download:
SaaS threat modeling guide →

A template opens as a preview, so nothing is added to your account until you click Save to my forests. Not on Pro yet? See plans.

When to move on

A template, or ThreatTree?

A file is a fine way to start. It stops scaling when the diagram and the register drift apart, or when someone else needs to read the result.

Free template filesdraw.io + spreadsheetThreatTree Free$0, 3 forestsThreatTree Pro$29/user/month
DFD, attack trees and a risk register✓ as separate files✓ linked in one forest✓ linked in one forest
A worked example to start from✓ one per file✓ a complete SaaS model✓ plus 3 industry models
Register built from your attack trees— copy rows by hand✓✓
STRIDE, OWASP, CAPEC and ATT&CK tagsTyped by hand✓✓
Risk register PDF—✓✓
Controls mapped to ISO 27001, NIST, SOC 2——✓
Team collaboration with rolesShare the files—✓
Industry templates and modules——✓
FAQ

Templates, answered

What people ask before downloading.

Want a template we don't have?

Tell us what you're modeling.

Suggest a template
Are these threat modeling templates really free?

Yes. The data flow diagram, attack tree and risk register templates are free downloads with no signup and no email gate, and you can use them for commercial work.

What opens a .drawio file?

draw.io (also called diagrams.net), either in the browser at app.diagrams.net or as the free desktop app, and the Draw.io Integration extension for VS Code. The risk register is a plain CSV that opens in Excel, Google Sheets, Numbers or LibreOffice Calc.

In what order should I use the templates?

Start with the data flow diagram to agree what the system is and where the trust boundaries are. Then build an attack tree for each threat that matters, and record every scored threat in the risk register with a mitigation and an owner.

Can I import the free templates into ThreatTree?

Not at the moment. The free files are for whatever tool you already use. In ThreatTree you build the same diagram and attack tree in the editors, and the risk register fills itself from the attack trees. The Pro industry templates open directly in ThreatTree.

What is included in the industry templates?

Each industry template is a worked example for a representative system: a data flow diagram, one to three attack trees with 3 to 16 scored risks that fill the risk register, and a downloadable register of 9 to 16 rows. There are nine: a fintech payment flow, a healthcare EHR, an AI agent pipeline, a connected vehicle, a connected insulin pump, a water treatment plant, an electricity grid control centre and substation, a pharmaceutical manufacturing plant and a multi-tenant B2B SaaS platform. They are included on the Pro and Enterprise plans and open in ThreatTree as a preview you can save to your forests.

Is there a STRIDE template?

Yes. The risk register template has a STRIDE category column with example rows covering all six categories, and the data flow diagram template gives you the elements to walk through STRIDE one by one.

Get new templates and threat-modeling guides by email as they're published — no more than one a week.